
Nguyen Hoang Loc goes by Beru
Notes from Ho Chi Minh City
I'm Nguyen Hoang Loc (Beru), a full-stack developer at Easy AI in Ho Chi Minh City. I write down what breaks in Claude Code, Next.js, AI crawlers and my own VPS, and how I fixed it.
Skip to writingWriting
Notes from things I ran myself, each with the version I tested.

Latest
All writingOAuth Today, DPoP Tomorrow: What MCP's August Roadmap Means for My Own MCP Server
On August 22, 2026, MCP's roadmap said agent identity should move past pasted API keys toward DPoP-bound tokens and Workload Identity Federation. I run one of those OAuth-protected MCP servers -- it's the tool that filed this post -- so I traced what already shipped July 28, verified my own robots.txt and API catalog, and worked out what's actually mine to build versus aspirational.

- Two Critical Next.js RCEs Shipped the Same Day: What I Actually Checked Before Patching My ServerNext.js & Prisma
- WebMCP Is Not MCP: I Tested Chrome's New Agent-Tool API With Google's Own PolyfillAI crawlers & llms.txt
- Claude Code Shipped --restricted Mode. Here's What It Actually Locks Down on My CMS RepoClaude Code
- Claude Code Shipped Model-Switch Hooks. Here's What They Actually Send When You Block OneClaude Code
- GPTBot Says It's GPTBot. I Stopped Taking Its Word for ItAI crawlers & llms.txt
Errors I've written up
Each one comes from a note on this site, next to what triggered it.

Topics
Each topic keeps its notes in one place, newest first.
Claude Code
11 notesThe coding agent I use every day. I install each release, run it against a real repository, and write down what broke or got blocked.
AI crawlers & llms.txt
8 notesHow GPTBot, ClaudeBot and other AI crawlers read the web, tested on this site with llms.txt, markdown pages and an OAuth-protected MCP server.
Next.js & Prisma
3 notesSecurity patches, breaking CLIs and new runtimes, landing on a self-hosted production site I maintain myself.

Building
Things I build and run myself, outside the day job.
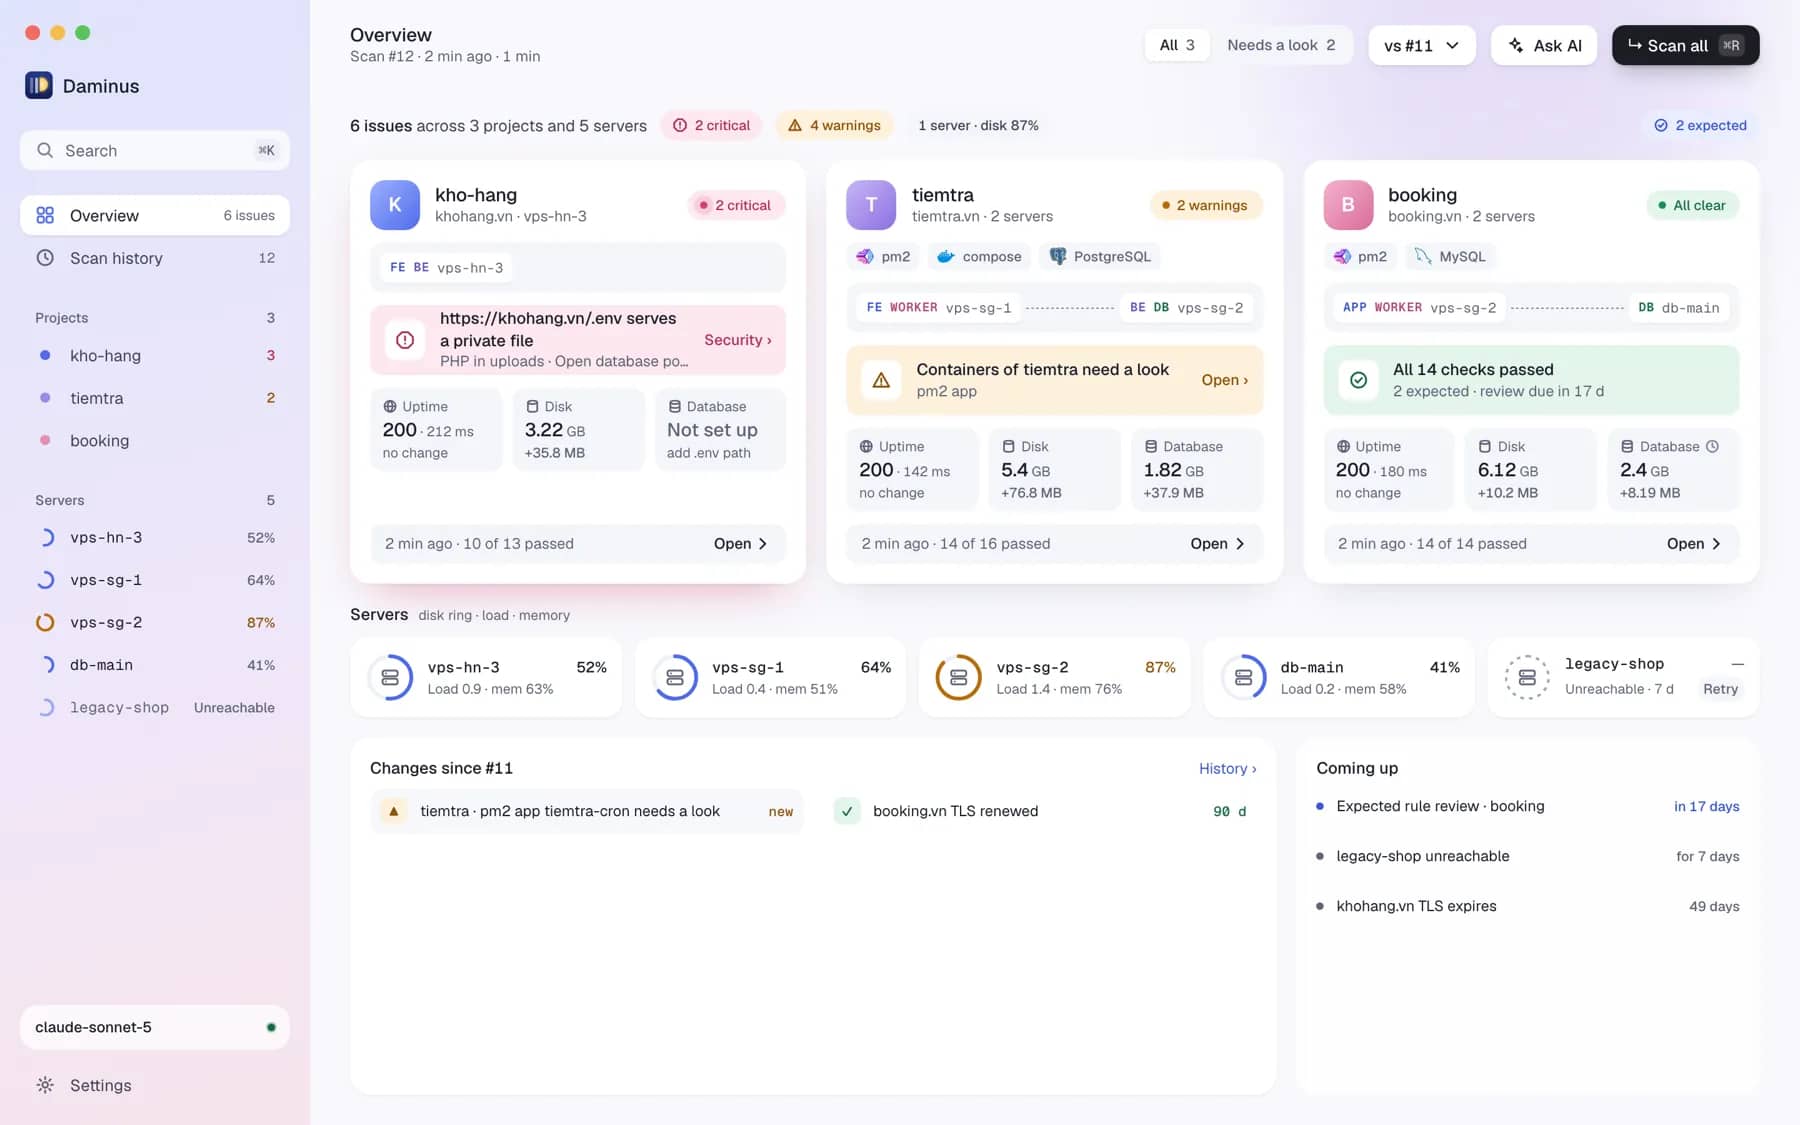
Daminus
Open source · MIT · macOS · v0.1.0
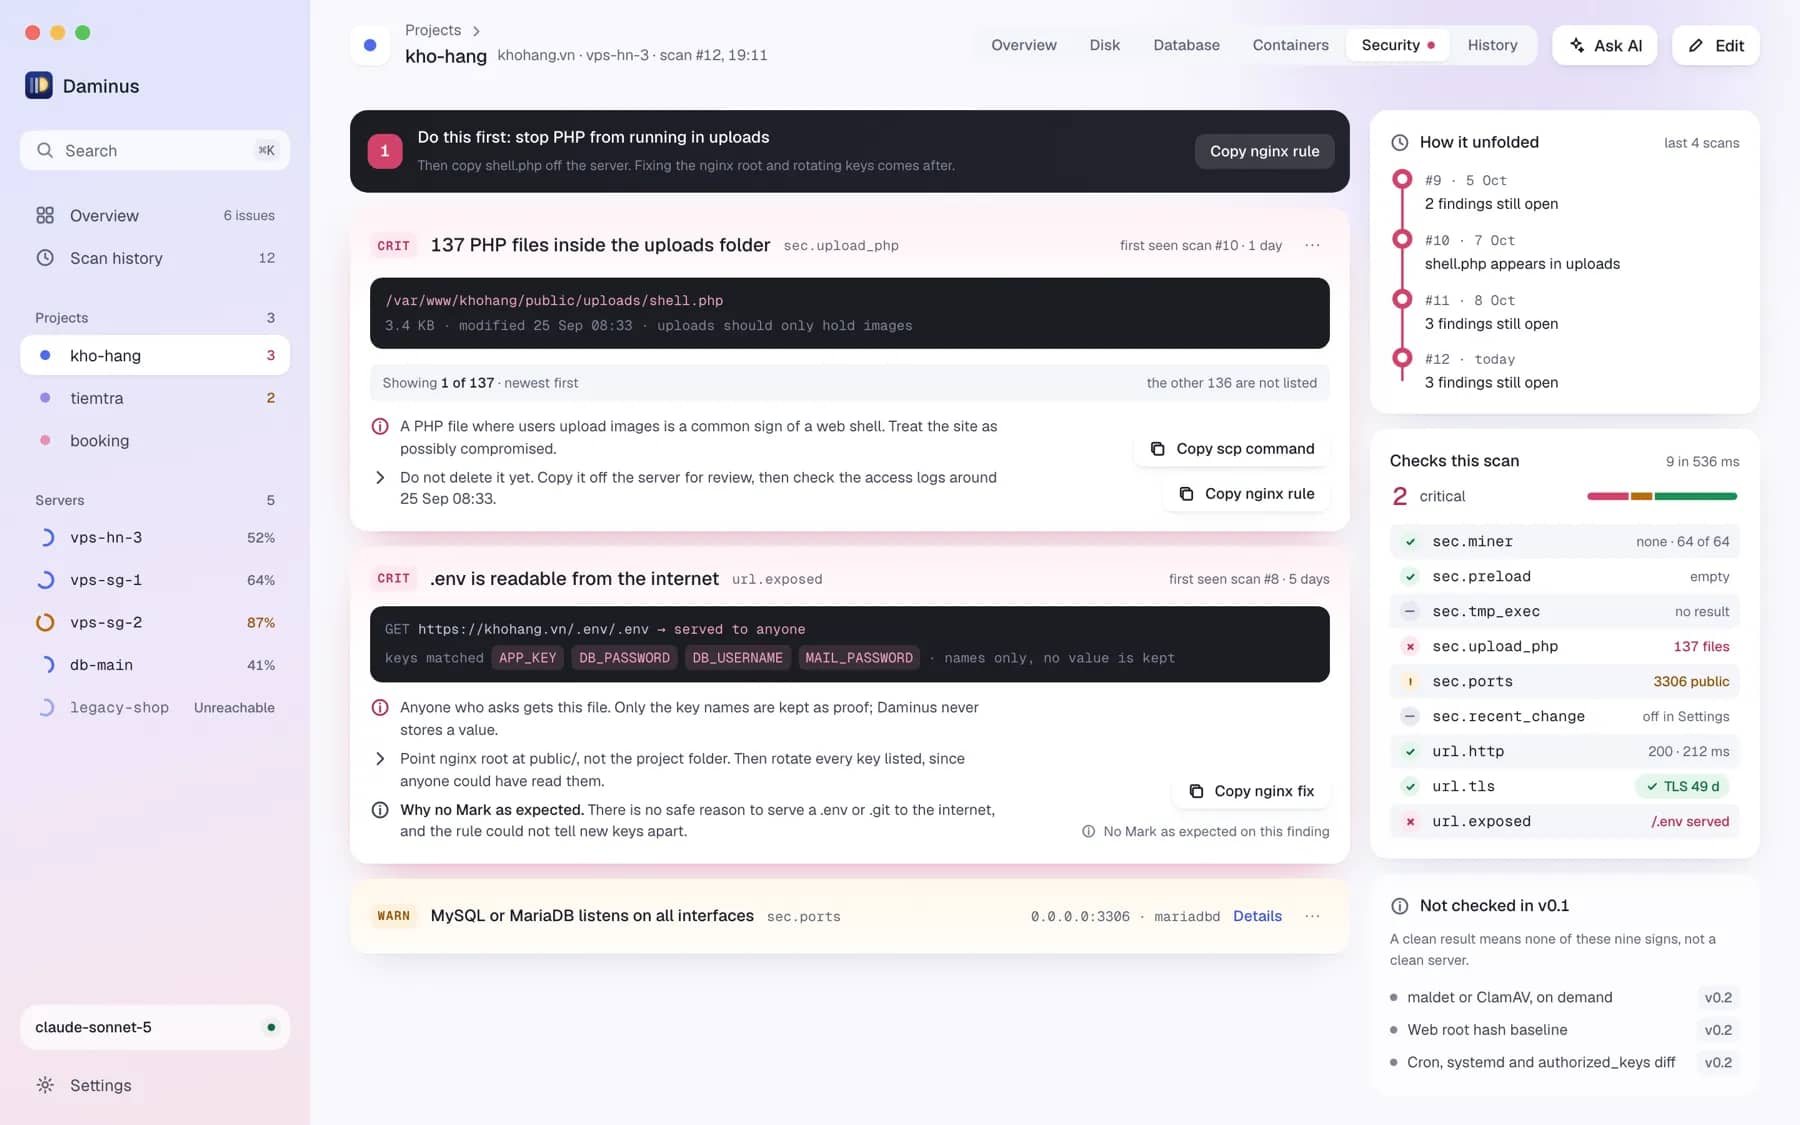
A Mac app that checks the servers behind your web projects over plain SSH. It installs nothing, only reads, and groups what it finds by project instead of by machine.
Your own SSH
agentlessIt uses your ssh and ~/.ssh/config, so ProxyJump, 1Password or Secretive agents and known_hosts behave as they do in your terminal.
Nothing written
read-onlyChecks only read. Nothing is written to or deleted from the server, and CI fails if a check tries.
One card each
per projectURL health, TLS expiry, disk, containers and pm2, database size, security signs.
No background jobs
on demandA scan is one SSH call per host, and it happens when you press the button.
AI review, off by default
optionalOff until you add a key: Anthropic, OpenAI, Gemini, DeepSeek, OpenRouter, a local Ollama, or any OpenAI-compatible endpoint.

About
I'm a full-stack developer at Easy AI, where I work on AI chatbot products from the frontend through the backend to the servers they run on. Outside work I run this site on my own VPS, build Daminus, and write down what I learn along the way.
- Based in
- Ho Chi Minh City, Vietnam
- Day job
- Full-stack developer, Easy AI
- Building
- Daminus, open source
- Writing about
- Claude Code, AI crawlers, Next.js
More about me. For project work, see services.